Architecture
An execution boundary for untrusted model proposals, typed validation, authorization, credentials, sandboxing, egress, approvals, and verification.
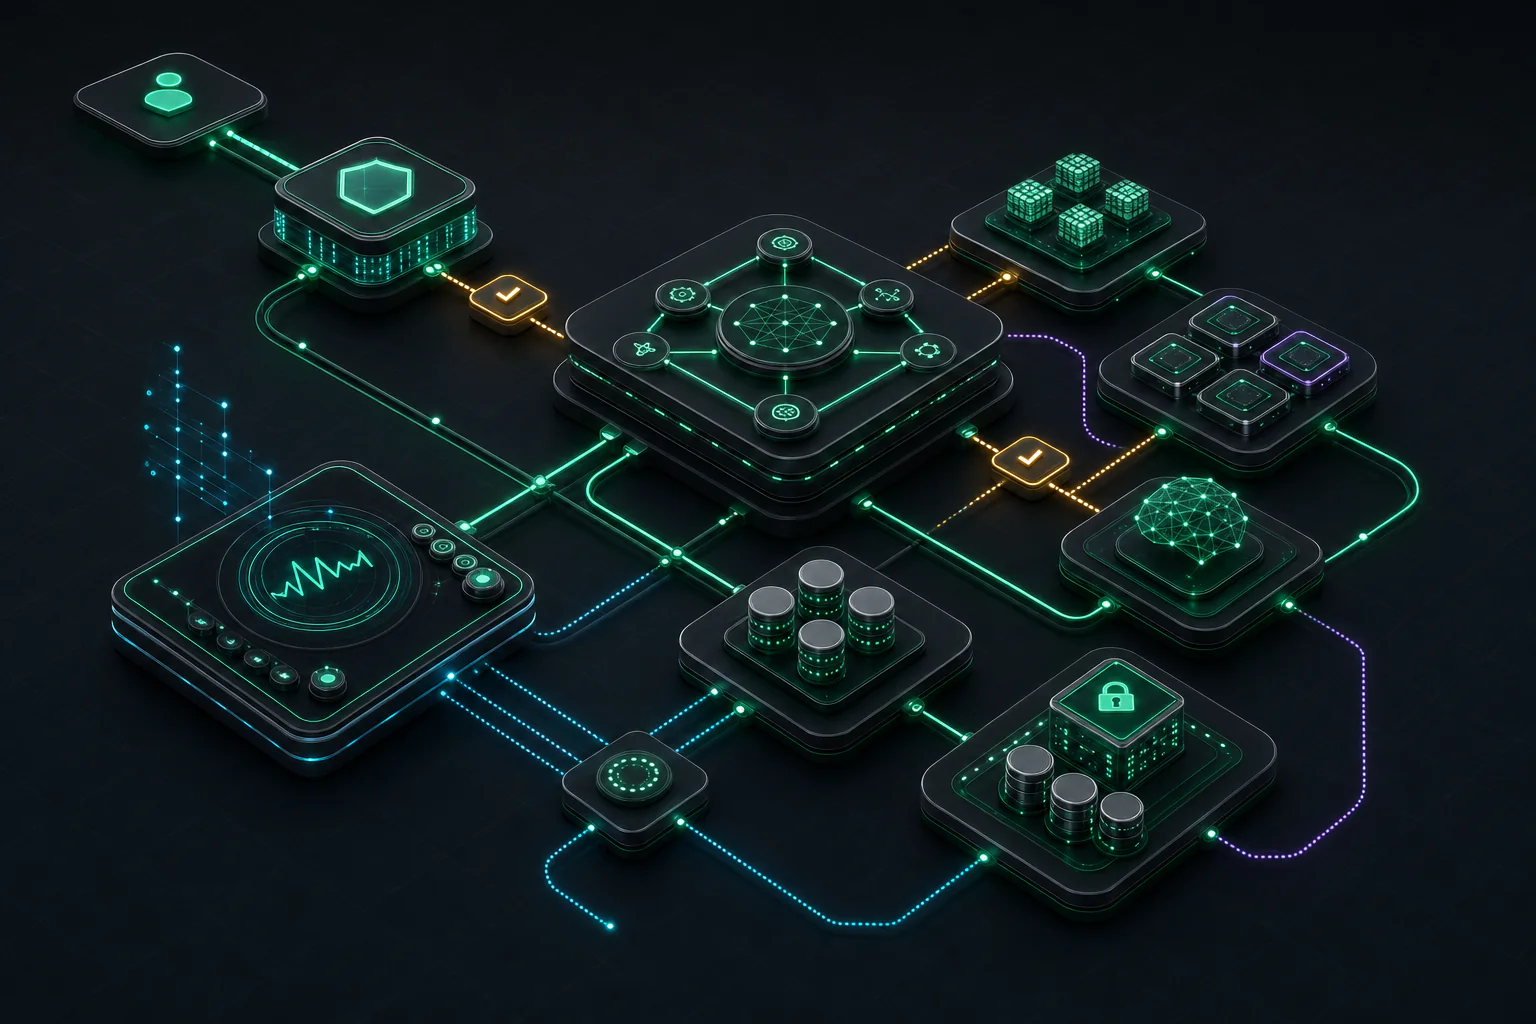
The architecture separates intent, policy, state, execution, evidence, and response. Each boundary has one accountable owner and an observable contract. Probabilistic components may propose or classify; deterministic software owns permissions, budgets, state transitions, and release conditions.
Decisions
| Decision | Required evidence | Review trigger | |---|---|---| | Treat model output and tool output as untrusted at different boundaries. | Versioned test, trace, or architecture record | Material workload, provider, policy, or data change | | Normalize and authorize exact parameters immediately before execution. | Versioned test, trace, or architecture record | Material workload, provider, policy, or data change | | Keep durable credentials outside model context. | Versioned test, trace, or architecture record | Material workload, provider, policy, or data change | | Verify effects through authoritative state, not tool prose. | Versioned test, trace, or architecture record | Material workload, provider, policy, or data change |
Alternatives and trade-offs
A centralized control plane simplifies policy and evidence collection but can become a latency and availability dependency. Distributed enforcement reduces central bottlenecks but requires consistent identity, versions, and audit semantics. Prefer the smallest boundary that can enforce the invariant and prove the outcome.
Failure modes
- Schema validation is mistaken for authorization.
- Containers mount host credentials or unrestricted networks.
- Approval tokens do not bind parameters.
- Tool output injects new instructions into the agent loop.
Operational checklist
- [ ] Unknown fields and ambiguous identifiers are rejected.
- [ ] Policy fails closed and carries tenant identity.
- [ ] Sandboxes restrict filesystem, process, network, and resources.
- [ ] Egress destinations and payloads are governed.
- [ ] Consequential actions have independent postcondition checks.
Connected practice
- Labs: /labs/prompt-injection-threat-model, /labs/agent-loop-tool-selection
- Projects: /projects/governed-agent-reliability
- System breakdowns: /systems/inside-openai-codex
Sources
owasp-llmmcp-specificationoauth-security-bcpnist-zero-trust
Continue Reading
All Blog PostsAttention Is All You Need Paper Breakdown: The Original Transformer Architecture
Technical paper teardown of Attention Is All You Need (Vaswani et al., NIPS 2017) detailing Scaled Dot-Product Attention math, Multi-Head Attention projections, Sinusoidal Positional Encoding, and KV cache memory bounds.
Autonomous Contract Redlining & Auditing in Enterprise M&A
How tier-1 corporate M&A teams deploy agentic LLM pipelines to analyze 10,000+ confidential deal documents under zero-data-retention VPC constraints and deterministic audit logging.
Balancing Cost, Latency, Reliability, and Security
Operational trade-offs must be measured at the successful user outcome, inside the same security and quality boundary.